Cybersecurity
Security Gaps Become Business Problems Quickly
Cyber incidents rarely begin with one obvious failure. Unpatched systems, weak access controls, overlooked alerts, and employee mistakes can combine into a costly disruption. Active oversight helps identify these gaps before they create more downtime, data exposure, or recovery work.
Unmonitored Threat Activity
Suspicious behavior can go unnoticed when no one is actively reviewing security activity across endpoints and networks. Delayed detection gives a potential incident more time to disrupt operations.
Unpatched Systems
Missing operating system and application updates can leave known weaknesses open to attack. Consistent patch management reduces exposure while helping systems remain stable and dependable.
Inconsistent Endpoint Protection
Laptops, desktops, and servers create multiple entry points into your business. Without coordinated endpoint detection and response, threats may be harder to identify and contain.
Poor Provider Responsiveness
Waiting for help during a security concern increases uncertainty and may allow the problem to spread. Businesses need clear communication and prompt action when unusual activity appears.
How Managed Cybersecurity Should Protect Your Operations
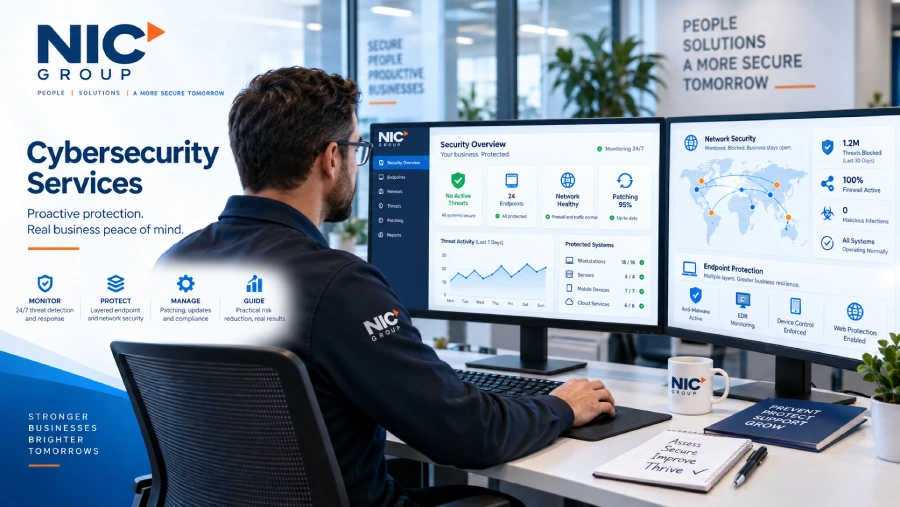
Effective cybersecurity depends on consistent visibility, layered safeguards, and a clear response plan. NIC Group manages the ongoing security work that internal teams often lack time to handle. This approach helps reduce avoidable exposure while keeping security aligned with day-to-day business needs.
Continuous Security Monitoring
Ongoing system and network monitoring helps surface unusual activity that warrants investigation. Our team reviews alerts and responds according to the nature and scope of the issue.
Layered Endpoint Defense
Endpoint detection and response, DNS filtering, and Windows security practices address threats at multiple points. These safeguards make it harder for one weakness to compromise the broader environment.
Managed Network Protection
Managed firewalls and secure network controls help regulate traffic entering and leaving your systems. Regular oversight keeps configurations aligned with changing operations and security priorities.
Practical Risk Guidance
We translate technical findings into clear business considerations without unnecessary jargon. You receive understandable recommendations that support informed decisions about risk, budget, and next steps.
Our IT Solutions & Services
Cloud Backup and Recovery
VoIP Business Solutions
AI Services & Support
Cybersecurity Services FAQs
What Is Included in NIC Group's Cybersecurity Services?
Services may include continuous monitoring, endpoint detection and response, DNS filtering, managed firewalls, patch management, security awareness training, and preparedness planning. The appropriate mix depends on your systems, users, risks, and existing controls. We begin by assessing your environment and identifying practical priorities.
Can Cybersecurity Eliminate Every Risk to My Business?
No cybersecurity program can eliminate every threat or prevent every incident. Layered safeguards, active monitoring, regular maintenance, and employee education can reduce exposure and improve response readiness. NIC Group focuses on managing risk in a practical, ongoing way.
How Does Endpoint Detection and Response Differ From Basic Antivirus Software?
Endpoint detection and response monitors activity on computers and servers for suspicious behavior, rather than relying only on known threat signatures. It provides greater visibility for investigating and containing potential incidents. NIC Group can incorporate EDR into a broader managed security approach.
How Quickly Can NIC Group Respond to a Cybersecurity Concern?
Response depends on the issue, its severity, and the services included in your plan. Clients can contact support by phone or submit a ticket through the online service system, and many issues can be investigated remotely. Specific service expectations are reviewed when selecting a package.
Do You Support Businesses with HIPAA or PCI Requirements?
NIC Group supports security controls, documentation, monitoring, and technology practices that may help businesses address HIPAA or PCI-related responsibilities. Compliance depends on operational, administrative, and legal factors beyond technology alone. We help identify relevant IT gaps without promising a specific compliance outcome.
What Happens When We Start Working with NIC Group?
The process begins with a discovery call to discuss your concerns, systems, and business needs. A security and network assessment can then identify gaps that may affect productivity or create unnecessary risk. We review the findings with you and outline clear options for moving forward.
Strengthen Your Cybersecurity Before the Next Incident
Schedule a consultation with NIC Group to discuss your cybersecurity concerns and review the safeguards currently protecting your business. We will help you identify practical next steps for reducing risk across your New Jersey technology environment.